 cPanel/WHM Plugins
TITAN Spam & Abuse Detection
A self-hosted spam & abuse detection and response platform for cPanel & WHM — detect outbound spam, PHP mail abuse, brute force and compromise, and respond automatically and reversibly.
- WHM & cPanel
- Encrypted code
- Signed packages
- English & Arabic
Price
$30 / year
One server, one year of updates and support. Renew whenever you like.
- Protected, signed package — verified before install
- Move the license to a new server yourself
- Full uninstall from the plugin or the command line
One command, as root
The installer checks your server, asks for your license key, verifies the signed package and installs it. The same command upgrades later.
# wget -O install.sh https://www.infinityinstaller.com/plugins/TITAN-Spam-Abuse-Detection/install.sh && bash install.sh
# bash install.sh --uninstall
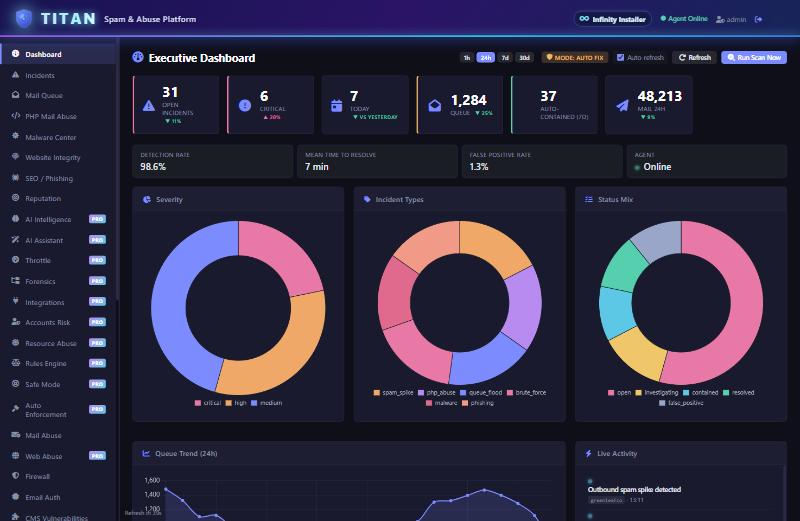
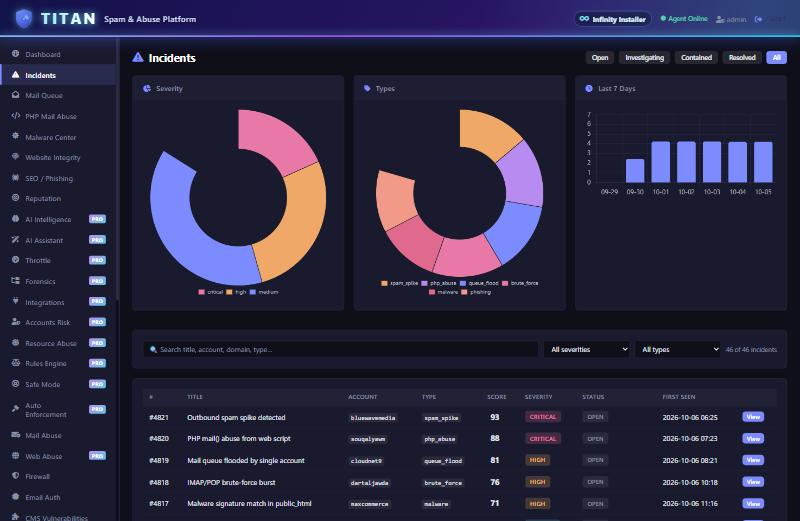
TITAN Spam & Abuse Detection in action
What TITAN Spam & Abuse Detection does
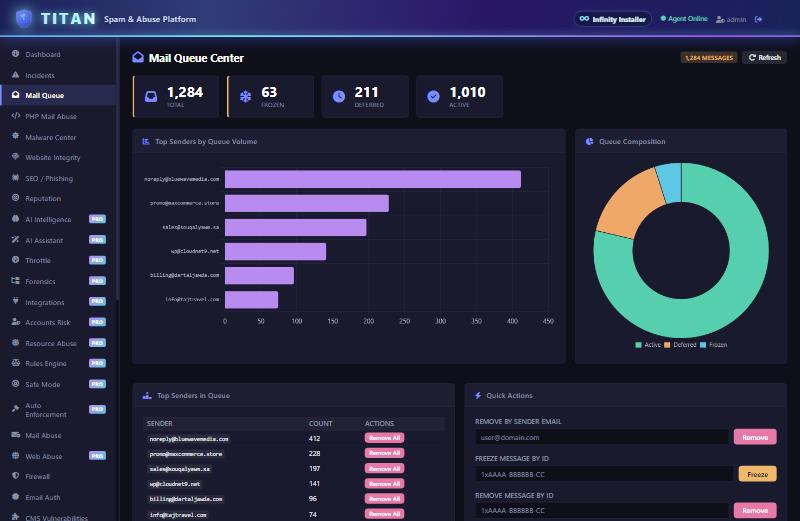
TITAN turns cPanel & WHM into a spam & abuse operations center. A self-hosted agent watches exim, auth and web logs in real time and scores every account for outbound spam, PHP mail abuse, brute force, resource abuse, CMS compromise, malware and SEO/phishing injections — with baselines, threat intelligence and AI triage.
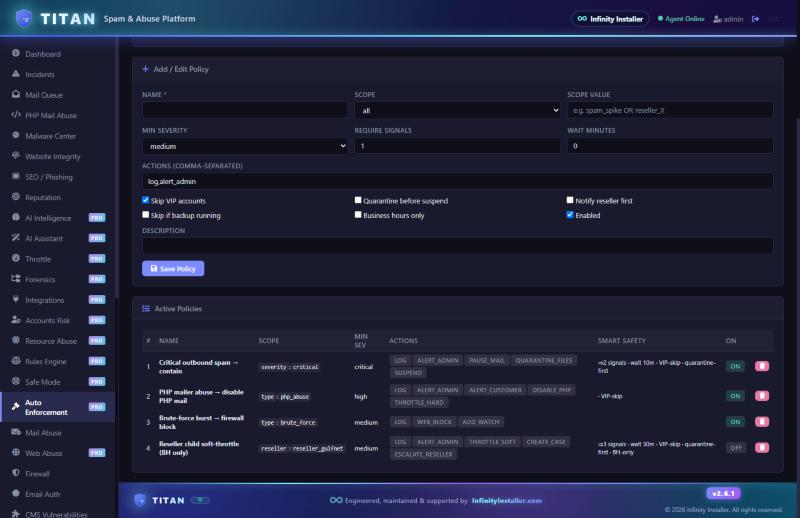
When something crosses the line, TITAN responds in graduated, fully reversible steps — throttle, safe-mode, firewall, quarantine — behind approvals, with action snapshots and rollback. A mail-queue center, deliverability/DNSBL reputation monitoring, email authentication and bounce-feed intelligence keep your IPs clean.
For operators there's a fleet hub across servers, an executive one-page report, a simulation/test mode to validate thresholds before enforcement, interactive response runbooks, incidents and forensic evidence bundles, an audit trail, RBAC, 2FA, and integrations (AbuseIPDB, Cloudflare, MISP, chat alerts) plus a WHMCS client view.
Self-hosted — the detection agent is a Python systemd service and the admin UI is a WHM/cPanel plugin. The PHP UI is ionCube-protected and the platform is licensed through InfinityInstaller.
Requirements
- cPanel & WHM server with root access; the TITAN agent runs as a systemd service.
- Python 3.8+ with the cryptography package (installed by install.sh); exim/dovecot/Apache logs.
- EA-PHP with ionCube Loader 15 (the encoded WHM/cPanel UI runs under ea-php84 via a cpsrvd proxy).
- Outbound HTTPS to infinityinstaller.com for license checks.
Features
- Real-time detection across exim/auth/web logs: outbound spam, PHP mail abuse, brute force, resource abuse, CMS compromise, malware, SEO/phishing injections.
- Risk scoring per account with an abuse scorer, baselines, threat intel and AI triage; repeat-offender and watchlist tracking.
- Graduated, reversible response: throttle, safe-mode, firewall, quarantine — with approvals, action snapshots and full rollback.
- Mail-queue center, deliverability/reputation (DNSBL) monitoring, email auth, and bounce-feed intelligence.
- Fleet hub for multi-server posture, an executive one-page report, simulation/test mode, and interactive response runbooks.
- Incidents, forensics evidence bundles, audit trail, RBAC, 2FA, integrations (AbuseIPDB, Cloudflare, MISP, chat alerts) and a WHMCS client view.
- Self-hosted Python agent (systemd) + WHM/cPanel admin UI; the PHP UI is ionCube-protected, licensed through InfinityInstaller.
You may also like
Churn & Client Intelligence
Predict churn, understand every client, and act — risk scoring, Client 360, sentiment AI, retention playbooks and executive analytics for WHMCS.
Enterprise Email Template Testing PRO
Test, preview and score every WHMCS email before it reaches a client — deliverability analyzer, quality gates, A/B subjects and batch suites.
Email Verification Pro
Verify every client email before they use your services — client-area lock, reminders, deliverability intelligence, fraud signals and analytics for WHMCS.